Aegis Compass™ | CDOR
Your Path to Cybersecurity & Digital Operational Resilience Under DORA, NIS2, NIST, & CS&R
Understand your cybersecurity and operational resilience posture across multiple jurisdictions through one harmonised framework.
Assess once, demonstrate compliance internationally.
Identify gaps. Prioritise action. Support regulatory dialogue with confidence.
Why Cybersecurity & Operational Resilience Matters
Cyber Threats Are Escalating
AI-powered attacks, ransomware, and data breaches strike faster than ever. Organisations need to know where their defences stand – before regulators ask.
Regulators Now Expect Demonstrable Resilience
Under DORA, NIS2, and CS&R, regulators expect organisations to show how resilience works in practice, not just that policies exist on paper.
Board-Level Confidence Is Now Mandatory
Operational resilience is not just an IT concern. Boards need clear, structured reporting that connects resilience investment to business continuity and regulatory expectations.
Confidence Without Measurement is Not Governance
Most boards report high confidence in their cyber oversight. But confidence without structured measurement is hope, not governance.
Many boards have run only one incident simulation in two years. The gap between what directors believe and what the organisation can show has become a strategic vulnerability.
The CDOR framework is designed to close that gap. It translates cyber and operational resilience posture into board-governable language. Structured domain insights, clear status indicators, and prioritised actions connect directly to risk appetite.
The result is not a set of technical KRIs that directors cannot govern. A structured, repeatable view of where resilience works, where it does not, and what to do about it.
The Challenge Facing Organisations Today
59%
59% of firms experienced at least one cyber attack in the past 12 months.
Most organisations still assess resilience in silos, domain by domain and jurisdiction by jurisdiction. Aegis Compass™ | CDOR provides what has been missing: a structured way to compare and prioritise.
33%
33% received significant regulatory fines after an attack.
Regulatory expectations are rising across every jurisdiction. Demonstrating resilience after an incident is harder than building it before one.
3x
IoT devices (33%), supply chain (28%), and cloud (27%) are the top attack entry points.
Resilience cannot be measured in a single domain. Attack surfaces span technology, suppliers, and infrastructure – and so does the CDOR framework.
Source: Hiscox Cyber Readiness Report 2025 (5,750 businesses across seven countries)
What is Aegis Compass™ | CDOR?
Aegis Compass™ | CDOR is a structured, repeatable assessment framework. It helps you understand, measure, and improve cybersecurity and digital operational resilience (CDOR). It works across jurisdictions, services, and regulatory regimes.
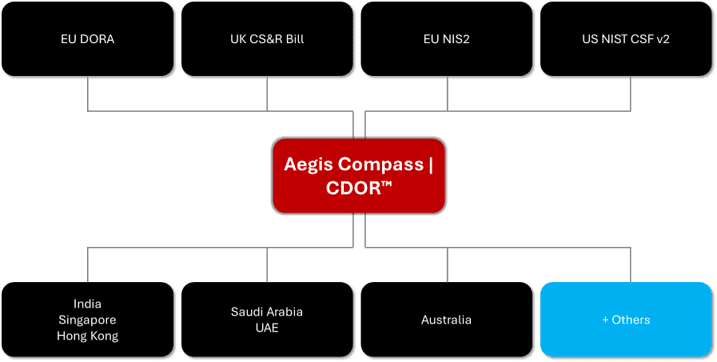
We deliver the CDOR framework through Argus Pro’s secure online platform, Aegis Compass. It assesses how your people, processes, and controls align to the expectations of regulators and standard-setting bodies. Those include DORA and its delegated RTS/ITS instruments, UK cyber and operational resilience reforms, and NIS2. Recognised frameworks such as ISO/IEC 27001, NIST CSF, COBIT 2019, and ITIL 4 are covered too.
The framework spans governance, prevention, detection, response, recovery, and continuous improvement. Assessment content is mapped at clause level to more than 180 LRG instruments across more than 25 jurisdictions.
The result is not a tick-box exercise. It is a clear, defensible view of where resilience works in practice, and where it does not.
- Assess baseline process maturity and process effectiveness
- Identify compliance gaps
- Prioritise remediation
- Track improvements over time
The CDOR framework captures perspectives from multiple respondents across seniority levels, functions, and locations. It surfaces gaps between how leadership believes resilience works and how it operates in practice.
More than 25 jurisdictions
Assessment content reflects cyber and operational resilience expectations across major financial, technology, and regulatory markets. They span the EU, UK, US, Asia-Pacific, Middle East, Africa, and Latin America.
More than 180 LRG instruments
Coverage spans primary legislation, delegated regulatory technical standards, supervisory guidance, and recognised international standards. All are mapped at the clause level.
Full incident lifecycle
Domains span the full incident lifecycle. That runs from governance and prevention, through detection, response, and recovery, to learning and improvement.
What the CDOR framework is and is not
The CDOR framework is
- A structured assessment of cyber and digital operational resilience across the full incident lifecycle
- A way to baseline, compare, and prioritise resilience improvements across services and jurisdictions
- A harmonised approach to mapping multiple regulatory expectations into a single, coherent view
- A framework designed to support informed regulatory dialogue, board reporting, and management decision-making
The CDOR framework is not
- Legal or regulatory advice
- A guarantee of regulatory compliance
- An audit, certification, or regulatory determination
- A one-size-fits-all solution
- A vendor selection or product endorsement tool
Argus Pro is not an auditor and does not provide audit opinions. The framework supports readiness, prioritisation, and improvement planning.
How The CDOR Framework Works
At a high level, the CDOR framework follows a simple, repeatable cycle:
Scope
Agree on relevant jurisdictions, critical services, resilience domains, and assessment boundaries.
Execute
Relevant stakeholders complete structured questions across the domains selected.
Score
Responses are assessed for maturity and effectiveness, highlighting strengths and vulnerabilities.
Prioritise
Findings are grouped and ranked to support proportionate remediation and investment decisions.
Report & Track
Interactive dashboards provide leadership with clear, focused views of resilience posture and progress over time.
What Makes Aegis Compass™ | CDOR Unique?
Who Can Use Aegis Compass™ | CDOR?
CISOs and Heads of Information Security
Understand where your resilience programme stands across every domain. Identify gaps that sit outside your traditional security perimeter, from third-party dependencies to organisational culture.
Chief Risk Officers
Integrate cyber and operational resilience into your enterprise risk framework, with quantified reporting that connects to risk appetite.
Heads of Operational Resilience
Map your important business services against the expectations of DORA, CS&R, NIST CSF, and others. See where dependencies and single points of failure exist.
General Counsel and Heads of Legal
Support regulatory defensibility with structured assessment outputs that demonstrate proportionate, risk-based approaches to resilience.
IT and Business Continuity Leaders
Baseline your recovery capabilities, infrastructure resilience, and disaster recovery readiness across the full incident lifecycle.
Risk Committees and Internal Audit
Use structured domain-level data to support risk-based planning, second-line challenge, and ongoing monitoring of resilience posture.
Boards and Non-Executive Directors
Move beyond technical KRIs with structured, comparable reporting. It distinguishes between having a policy and that policy working in practice.
Cyber Insurers and Underwriters
Support risk selection, pricing, and post-bind engagement with standardised resilience data that is consistent and comparable across jurisdictions.
The CDOR framework captures perspectives from multiple respondents across seniority levels, functions, and locations. It surfaces gaps between how leadership believes resilience works and how it operates in practice.
From "Unknown Unknowns" to Clear Priorities
Aegis Compass™ | CDOR doesn’t just highlight gaps. It provides:
- Domain-specific resilience insights across the full incident lifecycle
- Multi-respondent perspectives that surface gaps between leadership intent and operational reality
- A prioritised view of where to invest first for maximum impact
- Structured outputs that support regulatory conversations and board reporting
You Can Use The Framework To:
- Conduct cybersecurity and operational resilience health checks across business units and jurisdictions
- Prepare for DORA, NIS2, and CS&R regulatory engagement
- Assess third-party and supply chain resilience risk
- Support investment cases for cybersecurity controls and resilience capabilities
- Report cyber and operational resilience posture to the board and regulators
- Surface perception gaps between leadership and operational teams
- Identify knowledge gaps that represent hidden resilience risk
- Translate cyber and operational resilience posture into board-ready reporting. Replace ungovernable technical KRIs with structured domain insights that support governance and risk appetite conversations
- Support cyber insurance underwriting and renewal processes with standardised, repeatable resilience assessment data
So, What Should You Do?
Imagine answering your board, regulator, or investors with confidence. “We’ve assessed, understood, and improved our cybersecurity and digital operational resilience.”
That’s what Aegis Compass™ | CDOR delivers.
Take the first step today:
Explore Our Latest Insights
Practical guidance, regulatory updates, and real-world perspectives on building operational resilience with CDOR.
FAQs About Aegis Compass™ | CDOR
What is Aegis Compass | CDOR?
Aegis Compass is the name of our online platform for our compliance frameworks. CDOR, short for Cybersecurity & Digital Operational Resilience, is a comprehensive assessment framework that helps multi-jurisdiction organisations understand and improve their cyber and operational resilience posture.
The framework is mapped at clause level to more than 180 LRG instruments across more than 25 jurisdictions.
Does it align with industry standard frameworks?
Yes. The CDOR framework is designed to align with global legislation, regulation, and guidance, including the EU’s DORA (and all relevant delegated RTS/ITS instruments), the UK’s CS&R Bill and FCA/PRA operational resilience rules, NIST CSF 2.0 in the US, and Australia’s APRA CPS 230/234, as well as international standards such as ISO/IEC 27001, ISO 22301, COBIT 2019, ITIL 4, and the WEF’s 7 Pathways.
Is it a SaaS tool?
Aegis Compass is a secure online platform that enables multiple respondents from different teams, locations, or jurisdictions to complete the CDOR assessment. The assessment can also be delivered as a managed service.
Please contact us for further information.
Can I try before I buy?
Yes. You have two options: take a free version of the CDOR assessment via our website, or contact us to enquire about a pilot engagement covering one domain or one location to assess the framework, the Aegis Compass platform, and the value of the insights provided.
How long does an assessment take?
Assessment duration depends on the scope. Per respondent, a typical single-domain assessment could be completed between 30 minutes and 1 hour.
A full 26-domain assessment can be completed across multiple sessions over several days. The platform supports save-and-resume, so respondents can work at their own pace.
Who should complete the assessment?
The CDOR framework is designed for multi-respondent assessment. Depending on the scope, respondents typically include CISOs, Heads of Operational Resilience, IT and Business Continuity leaders, Risk and Compliance professionals, and relevant first-line operational staff.
The framework captures perspectives from different seniority levels, functions, and locations to provide a rounded view of resilience.
Do I have to assess every domain?
No. The framework is modular. You can start with a 'Priority Domains' assessment covering the domains most relevant to your organisation, for example, board governance and oversight, incident response, third-party risk, and regulatory compliance. A 'Priority Domains' assessment can typically be completed in one to three hours. Organisations can use this as a starting point before expanding to a full assessment.